
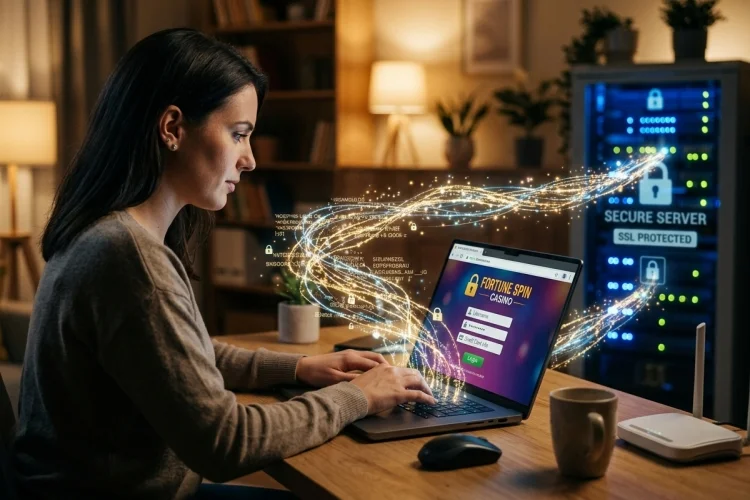
When you log in to an online casino, your browser may send passwords, account details, payment information, and other sensitive data across the internet. Sending that information without encryption would create an obvious security risk.
Understanding How SSL Encryption Protects Casino Players explains why HTTPS has become a basic requirement for websites handling private information.
Modern websites technically use TLS rather than the older SSL protocol, but the term “SSL encryption” remains widely used. The technology helps protect information while it travels between your browser and the casino’s server.
What Is SSL Encryption?
SSL stands for Secure Sockets Layer. It was originally created to establish encrypted and authenticated connections between computers communicating over the internet.
However, the original SSL protocols are now outdated. Modern secure websites use Transport Layer Security, or TLS, which replaced SSL and provides stronger cryptographic protection. The terms SSL, TLS, and SSL/TLS are still frequently used interchangeably in everyday discussions.
When a casino uses HTTPS, TLS encrypts information exchanged between the website and the player’s browser.
Instead of sending readable information directly across the network, the connection transforms it into encrypted data that unauthorized observers should not be able to understand.
How Encryption Protects Login Details
Your username and password are among the first pieces of sensitive information sent when accessing an online casino account.
Without an encrypted connection, someone capable of monitoring network traffic could potentially intercept data transmitted in plain text. TLS significantly reduces this risk by encrypting the communication before it travels across the network.
OWASP identifies confidentiality as one of the main security benefits of TLS because it prevents attackers from simply reading intercepted web traffic.
This protecion is particularly useful when users connect through networks they do not completely control, such as hotel, airport, café, or other shared Wi-Fi networks.
Encryption does not make those networks trustworthy, but it helps prevent the data travelling through them from being easily exposed.
SSL/TLS Helps Secure Payment Information
Casino players may also transmit financial information when making deposits or withdrawals.
Depending on the payment method, this could involve card information, account details, transaction identifiers, or data exchanged with an external payment provider.
TLS protects this information while it is in transit.
PCI Security Standards Council guidance states that cardholder data transmitted over open or public networks must be protected with strong cryptography and secure protocols.
For example, suppose someone enters payment information on a properly configured HTTPS page. The browser and server communicate through an encrypted channel rather than transmitting those details as easily readable text.
That makes interception considerably harder.
How the TLS Handshake Creates a Secure Connection
The encryption process begins before sensitive account information is exchanged.
When your browser connects to an HTTPS casino website, it performs what is commonly called a TLS handshake. During this process, the browser and server agree on cryptographic settings and establish keys that will secure the session.
The server also presents a digital certificate.
That certificate helps the browser verify that it is communicating with the intended domain rather than an unrelated server pretending to be that website. Cloudflare describes SSL/TLS as providing encryption, authentication, and protection against data tampering.
After the handshake is completed, the browser and server can exchange encrypted information efficiently.
The technical process happens very quickly, so most players never notice it.
Certificates Help Verify the Website
Encryption alone is only part of secure communication.
A website also needs to prove its identity to the browser. Digital certificates help perform that role.
A trusted certificate normally contains information connecting the cryptographic identity of the server with its domain name. Browsers evaluate that certificate against trusted certificate authorities.
If the certificate is expired, invalid, or issued for a different domain, modern browsers can display a warning.
OWASP recommends certificates issued by trusted authorities and stresses that the domain name in the certificate should correctly match the server being accessed.
This authentication layer can make certain impersonation attacks more difficult.
TLS Helps Prevent Data Tampering
Another important benefit is integrity.
A secure connection should not only hide information from outsiders. It should also help prevent data from being silently modified while travelling between the player and server.
OWASP describes integrity as protection against unauthorized modification of traffic.
Imagine submitting an account request through an insecure connection. An attacker positioned between the browser and server might attempt to manipulate part of that traffic.
TLS uses cryptographic mechanisms that help detect unauthorized changes.
This creates something similar to a digital tamper seal around network communication.
HTTPS Can Protect Casino Sessions
Security continues after login.
Websites usually rely on session identifiers or cookies to remember that a user has authenticated. Protecting those session tokens is important because someone who obtains a valid session token could potentially attempt to impersonate the logged-in user.
OWASP recommends using encrypted HTTPS connections for the entire web session rather than protecting only the login page.
Secure cookies can also be configured so that browsers transmit them only through encrypted HTTPS connections.
A casino that protects its login page but allows other account pages to communicate through unsecured HTTP would create an unnecessary risk.
Modern sites should therefore apply TLS consistently across the entire platform.
SSL Encryption Does Not Make a Casino Trustworthy
One common misunderstanding is assuming that HTTPS automatically proves a website is legitimate.
It does not.
A fraudulent website can potentially obtain its own valid certificate. HTTPS means your connection to that domain is encrypted; it does not guarantee that the business behind the domain is honest, licensed, financially stable, or safe to use.
Players should still verify the exact website adress, licensing details, operator identity, security policies, and reputation.
Encryption should be viewed as one security layer rather than a complete trust certificate.
What SSL/TLS Cannot Protect
TLS mainly protects information travelling between two endpoints.
Once information reaches the casino’s server, other security controls become responsible for protecting it.
OWASP specifically notes that TLS does not protect sensitive data after it has reached the receiving system.
Server breaches, weak passwords, phishing, malware, compromised employee accounts, insecure databases, and poor access control require seperate protections.
That means a secure casino platform should combine TLS with strong account security, secure data storage, authentication controls, monitoring, and responsible payment processing.
Players also have a role to play. Using unique passwords and avoiding suspicious links can reduce risks that encryption alone cannot solve.
Which TLS Versions Should Modern Sites Use?
Not every version provides the same level of security.
SSL 2.0 and SSL 3.0 contain serious weaknesses and should no longer be used. TLS 1.0 and TLS 1.1 have also been formally deprecated.
OWASP currently recommends TLS 1.3 by default while allowing TLS 1.2 when compatibility requires it.
Players do not normally need to configure these protocols manually because modern browsers and properly configured servers negotiate secure versions automatically.
Still, browser certificate warnings or insecure HTTP pages should not simply be ignored.
Understanding How SSL Encryption Protects Casino Players starts with recognizing what TLS does best: encrypting data, authenticating servers, and protecting information from tampering during transmission.
It can secure logins, payments, and active sessions, but it cannot guarantee that a casino itself is trustworthy. Before entering sensitive information, check for HTTPS, verify the domain carefully, and review the operator’s wider security practices.
